AWS EKS Security Masterclass with OWASP EKS Goat
Attack a deliberately vulnerable EKS cluster with OWASP EKS Goat: lift credentials via IMDSv2, enumerate ECR and backdoor an image, then break out from pod to node. Apply the RBAC, network policy and GuardDuty fixes that would have stopped you.
OWASP EKS Goat is an official OWASP project, delivered as a training and presented at:
- Format
- Online, live
- Labs
- Browser-based
- Next batch
- Not scheduled
We will write once, when a date is set.
About this training
Built on OWASP EKS Goat, an intentionally vulnerable EKS cluster. You deploy it, break it the way an attacker would, and then put the controls back.
The path runs end to end: exploit the sample application, use IMDSv2 to lift credentials, enumerate ECR with them, backdoor an image, move into the cluster, break out from pod to node, escalate into S3, and then clean up. The defensive half covers automated scanning and threat detection.
What you’ll do
19 labs and 8 theory sessions across 8 sections. Theory appears where it is needed for the next lab, not as a lecture block.
01Setup
- labSet up an AWS IAM user
- labSet up a GitHub Codespace
02Introduction to Docker
- labDocker working
- theoryDocker namespaces and control groups
- theoryDocker images and layers
- theoryDocker secrets
- theoryStatic analysis of Docker containers (SAST)
- labUsing Dockle and Hadolint
- labAudits with Aqua Security Docker Bench
03AWS Elastic Container Registry
- labECR image scanning
- theoryECR immutable image tags
04AWS EKS fundamentals
- labDeploying a vulnerable AWS EKS infrastructure
- theoryKubernetes architecture
- theoryAWS EKS terminologies
- theoryEKS authentication and authorisation
05Exploiting the sample application
- labEnumerate and exploit the web application
- labUsing IMDSv2 to exfiltrate credentials
- labEnumerate ECR repositories with those credentials
- labBackdooring a Docker image
- labExploiting the AWS EKS cluster
- labBreaking out from pod to node
- labPrivilege escalation and S3 exploitation
- labCleanup of the EC2 instance
06Automated scanning in EKS
- labScanning with Kubescape
- labScanning with kube-bench
07Defense and hardening in EKS
- labAWS GuardDuty for threat detection
08Teardown
- labDestroy the vulnerable EKS infrastructure
Work through it yourself
The complete walkthrough is public, and OWASP EKS Goat is an official OWASP project. Work through it at your own pace, or use it to revisit the labs afterwards.
eksgoat.peachycloudsecurity.com →Read the prerequisites before you book.
Some trainings require you to bring your own cloud account (AWS, GCP, or both) with billing enabled and admin privileges. Labs will not run without it, so confirm you meet every prerequisite below before the session.
Hard requirement for corporate laptops: admin permission to install tools, endpoint security and antivirus disabled, and the required lab domains not blocked on your network. Confirm this with your IT team before you register - troubleshooting a locked-down laptop mid-session is not possible.
How our trainings run
- Live and instructor-led, with the trainers in the room rather than a recording.
- Labs run in the browser. Nothing to install, and no fight with a corporate laptop.
- Attack first, then fix. Every exploited flaw is followed by the control that stops it.
- You keep the material and a certificate of completion.
Who runs it
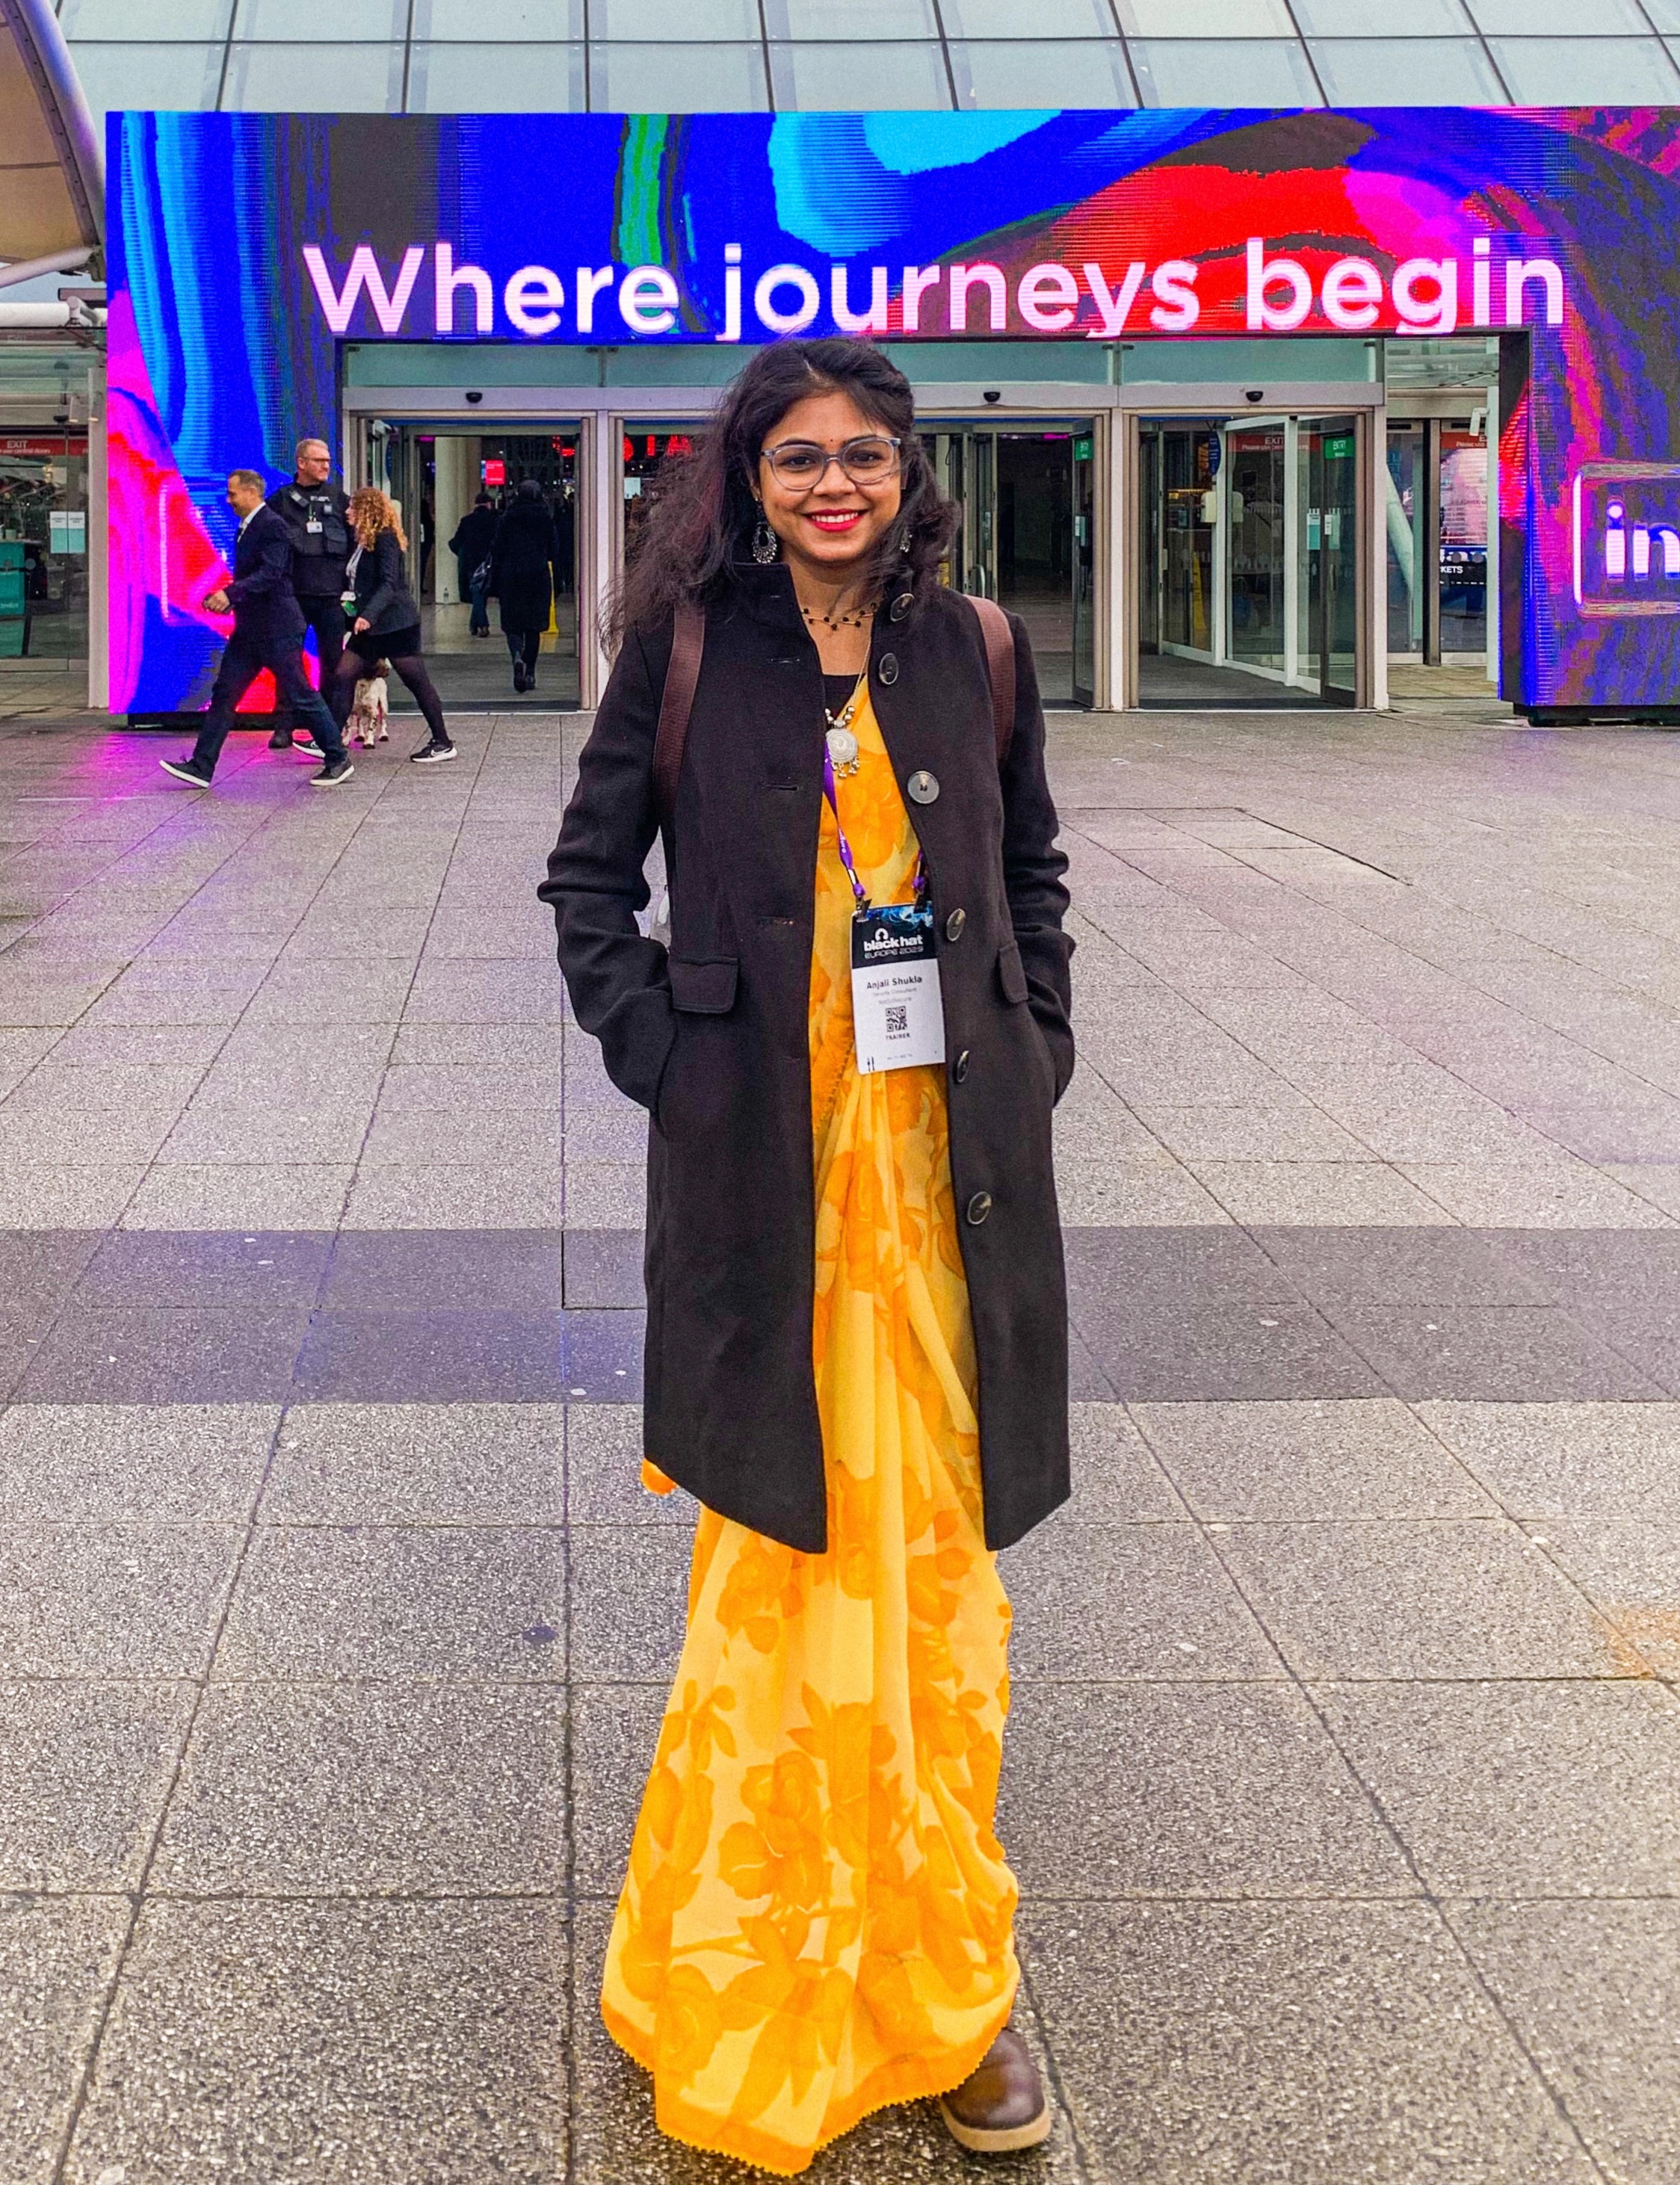
Anjali Shukla
Senior Security Engineer · Black Hat and Nullcon trainer
Founder, Container Security Village. OWASP EKS Goat lead. AWS Community Builder. Women Influencer in Cloud Security, CSA Bangalore 2023. Leads the W3-CS Bengaluru chapter.
Want a seat when it runs?
This batch is not scheduled yet. Join the waitlist and we will write the moment a date is set.
Support Our Work
Subscribe, like, and share our videos.
No Spam. Only updates.