Practical Security Engineering for Tech Teams
OWASP Top 10, Containers, DevSecOps, AWS Security, AI Security and AI-Assisted Security Reviews. All labs in the browser, no local setup
Per participant
Up to 50% off discounted pricing available
Your rate depends on eligibility (see below). Early bird ends 30 September 2026.
- Early bird: 20% off
- first 10 seats*
- Student / fresher: 50% off
- student id or <2 years experience*
- Group: 10% off
- 3 or more booking together*
Biggest discount
- Discounts are granted at our discretion (proof required) and don’t stack. See terms.
- Request a code: hello@peachycloudsecurity.com · LinkedIn
About this training
Security vulnerabilities slip into production faster than teams can catch them. This 2-day workshop teaches developers, DevOps engineers, SREs, and security engineers to identify and remediate vulnerabilities across web applications, containers, cloud infrastructure, and AI/LLM applications. Learn to attack OWASP Top 10 vulnerabilities, exploit containers and harden images, attack AWS misconfigurations across multiple cloud services, integrate automated security testing into CI/CD pipelines via GitHub Actions and Jenkins, secure LLM applications against prompt injection, and then apply threat modelling to realistic architectures.
This workshop takes a progressive, hands-on approach. You will learn to attack OWASP Top 10 vulnerabilities, perform secure code review, exploit container isolation weaknesses, harden container images and supply chains, attack and secure AWS cloud infrastructure, automate vulnerability scanning and static analysis, integrate security into CI/CD workflows, secure LLM systems against prompt injection and RAG pipeline poisoning, and apply STRIDE threat modelling to web, cloud, and AI architecture.
All labs run in a browser-based environment with no local installation required. You leave with the full mdbook, a certificate of completion, and complete lab documentation for ongoing reference and practice.
Who this is for
Does one of these read like your own week?
- You write and ship code, and keep getting security findings you cannot reproduce locally.
- You own the pipeline and have been asked to “add security scanning” with no brief beyond that.
- You run AWS or Kubernetes in production and have never attacked your own environment.
- You are moving into security from dev, ops or SRE and need hands-on proof, not just theory.
- You already review designs and want the whole attack chain end to end, not one flaw at a time.
If so, this training is for you.
What you’ll do
46 labs across 10 sections. Theory appears where it is needed for the next lab, not as a lecture block.
Day 1
01OWASP Top 10 (2025) Pentesting
- labSet up the vulnerable app in Codespaces
- labBurp Suite Community usage
- labA01 Broken Access Control
- labA02 Cryptographic Failures
- labA03 Injection
- labA04 Insecure Design
- labA05 Security Misconfiguration
- labA06 Vulnerable and Outdated Components
- labA07 Identification and Authentication Failures
- labA08 Software and Data Integrity Failures
- labA09 Security Logging and Monitoring Failures
- labA10 Server-Side Request Forgery
- labClean up the vulnerable app
02Secure Code Review
- theoryReading code for injection and SSRF flaws
- labOS command injection in Maintenance
- labServer-side request forgery in Maintenance
03Automated Source Code Review
- theoryStatic analysis in the review workflow
- labScanning with Opengrep
04Container Security
Container fundamentals
- theoryLinux namespaces and isolation
- labExploring namespace isolation
- theoryControl groups and resource limits
- labPreventing resource exhaustion
Runtime and privilege security
- theoryPrivileged vs non-privileged containers
- labPrivilege escalation and container escape
- theoryRoot vs non-root execution
- labRead-only root filesystem
- theoryLinux capabilities and seccomp
- labDropping unnecessary capabilities
Image security
- theoryVulnerable vs secure base images
- labScanning images with Trivy
Secrets and image layers
- theorySecrets in image layers
- labExtracting secrets from images
- labMoving secrets from env vars to secure mounts
05Infrastructure as Code and its benefits
- labStatic IaC scanning with Checkov
Day 2
06Software Composition Analysis (SCA)
- theoryDependency risk and transitive vulnerabilities
- labSoftware composition analysis in Python (pip-audit)
- labRemediating insecure dependencies
- labContainer SBOM with Syft and Grype
- labTransitive dependency analysis
07DevSecOps
One Jenkins pipeline, built up stage by stage
- theoryCICD security with Jenkins
- labSet up the pipeline and add a secret scanning stage
- labAdd a SAST stage
- labAdd an SCA stage
- labAdd a DAST stage with ZAP and OSS Vulnerability Management
08AWS Cloud Security
- theoryIAM policies, roles and privilege escalation paths
- labBasics of IAM policies
- labOverly permissive IAM policies
- labAttacking S3 buckets
- labAttacking AWS WAF
- labEC2 & ALB security
- labAWS misconfiguration challenges
09AI Security
- theoryPrompt injection
- labAI prompt injection
- labDefending prompt injection with LLM Guard
- theoryRAG pipeline poisoning
- labPoisoning a RAG pipeline
- labRAG pipeline defence
- theoryAI BOM
- labGenerating an AI BOM
10Threat Modelling & Security Review
- theoryThreat modelling and security review
- labThreat modelling and security review of a FinTech application
- labAssisted security review using Claude skills
Why this one
Labs, not slides
46 named labs across 10 sections. Theory appears where it is needed to do the next lab, not as a lecture block.
Nothing to install
Everything runs in GitHub Codespaces in a browser. No Docker on your laptop, no VM, no corporate-laptop fight.
Attack and then fix
Every exploited flaw is followed by the remediation, so you leave with both halves rather than a list of scary demos.
You keep the book
The full mdbook stays with you after the training, so the labs are repeatable when you actually need them at work.
What this training does not cover
- A guaranteed job, promotion, or salary bump. The certificate proves you did the work; it does not replace doing the work at your job.
- A magic fix for your organisation's security posture. You leave with a working method, not a finished audit of your company.
- Coding from scratch or a data science course. Labs use realistic, deliberately vulnerable applications you attack and fix, not applications you build.
- One-on-one mentoring during the batch. Instructors run the room; book a 1:1 session separately for individual coaching.
What you need
Read the prerequisites before you book.
Some trainings require you to bring your own cloud account (AWS, GCP, or both) with billing enabled and admin privileges. Labs will not run without it, so confirm you meet every prerequisite below before the session.
Hard requirement for corporate laptops: admin permission to install tools, endpoint security and antivirus disabled, and the required lab domains not blocked on your network. Confirm this with your IT team before you register - troubleshooting a locked-down laptop mid-session is not possible.
- AWS access: where a lab needs AWS, we provide pre-created credentials and environments as per that lab's requirement.
- Access and kit: a GitHub account, a laptop with a modern browser (Chrome, Firefox, or Edge), at least 4GB RAM, and a stable internet connection. No local Docker or tool installation needed.
- Mindset: curiosity and the willingness to research when you get stuck. Trainers guide every lab, and the material stays with you to revisit and extend afterwards.
- Technical comfort: familiarity with the command line and following step-by-step instructions is enough. No prior pentesting or container experience required.
- Environment: on Windows or Mac, make sure endpoint security, antivirus, and VPN are not blocking browser access to GitHub.
- Codespace access verified before day 1, using the setup instructions sent after registration.
What you keep
- Certificate of completion
- Issued after you complete the training.
- Full mdbook
- Theory and every step-by-step lab, yours to keep and revisit.
- Interview question repository
- The cloud security interview question set we maintain.
- Monthly career workshop
- A free group workshop every month for anyone who has attended a Peachycloud training. Resume reviews, mock interviews, interview questions - the topic rotates.
Who runs it
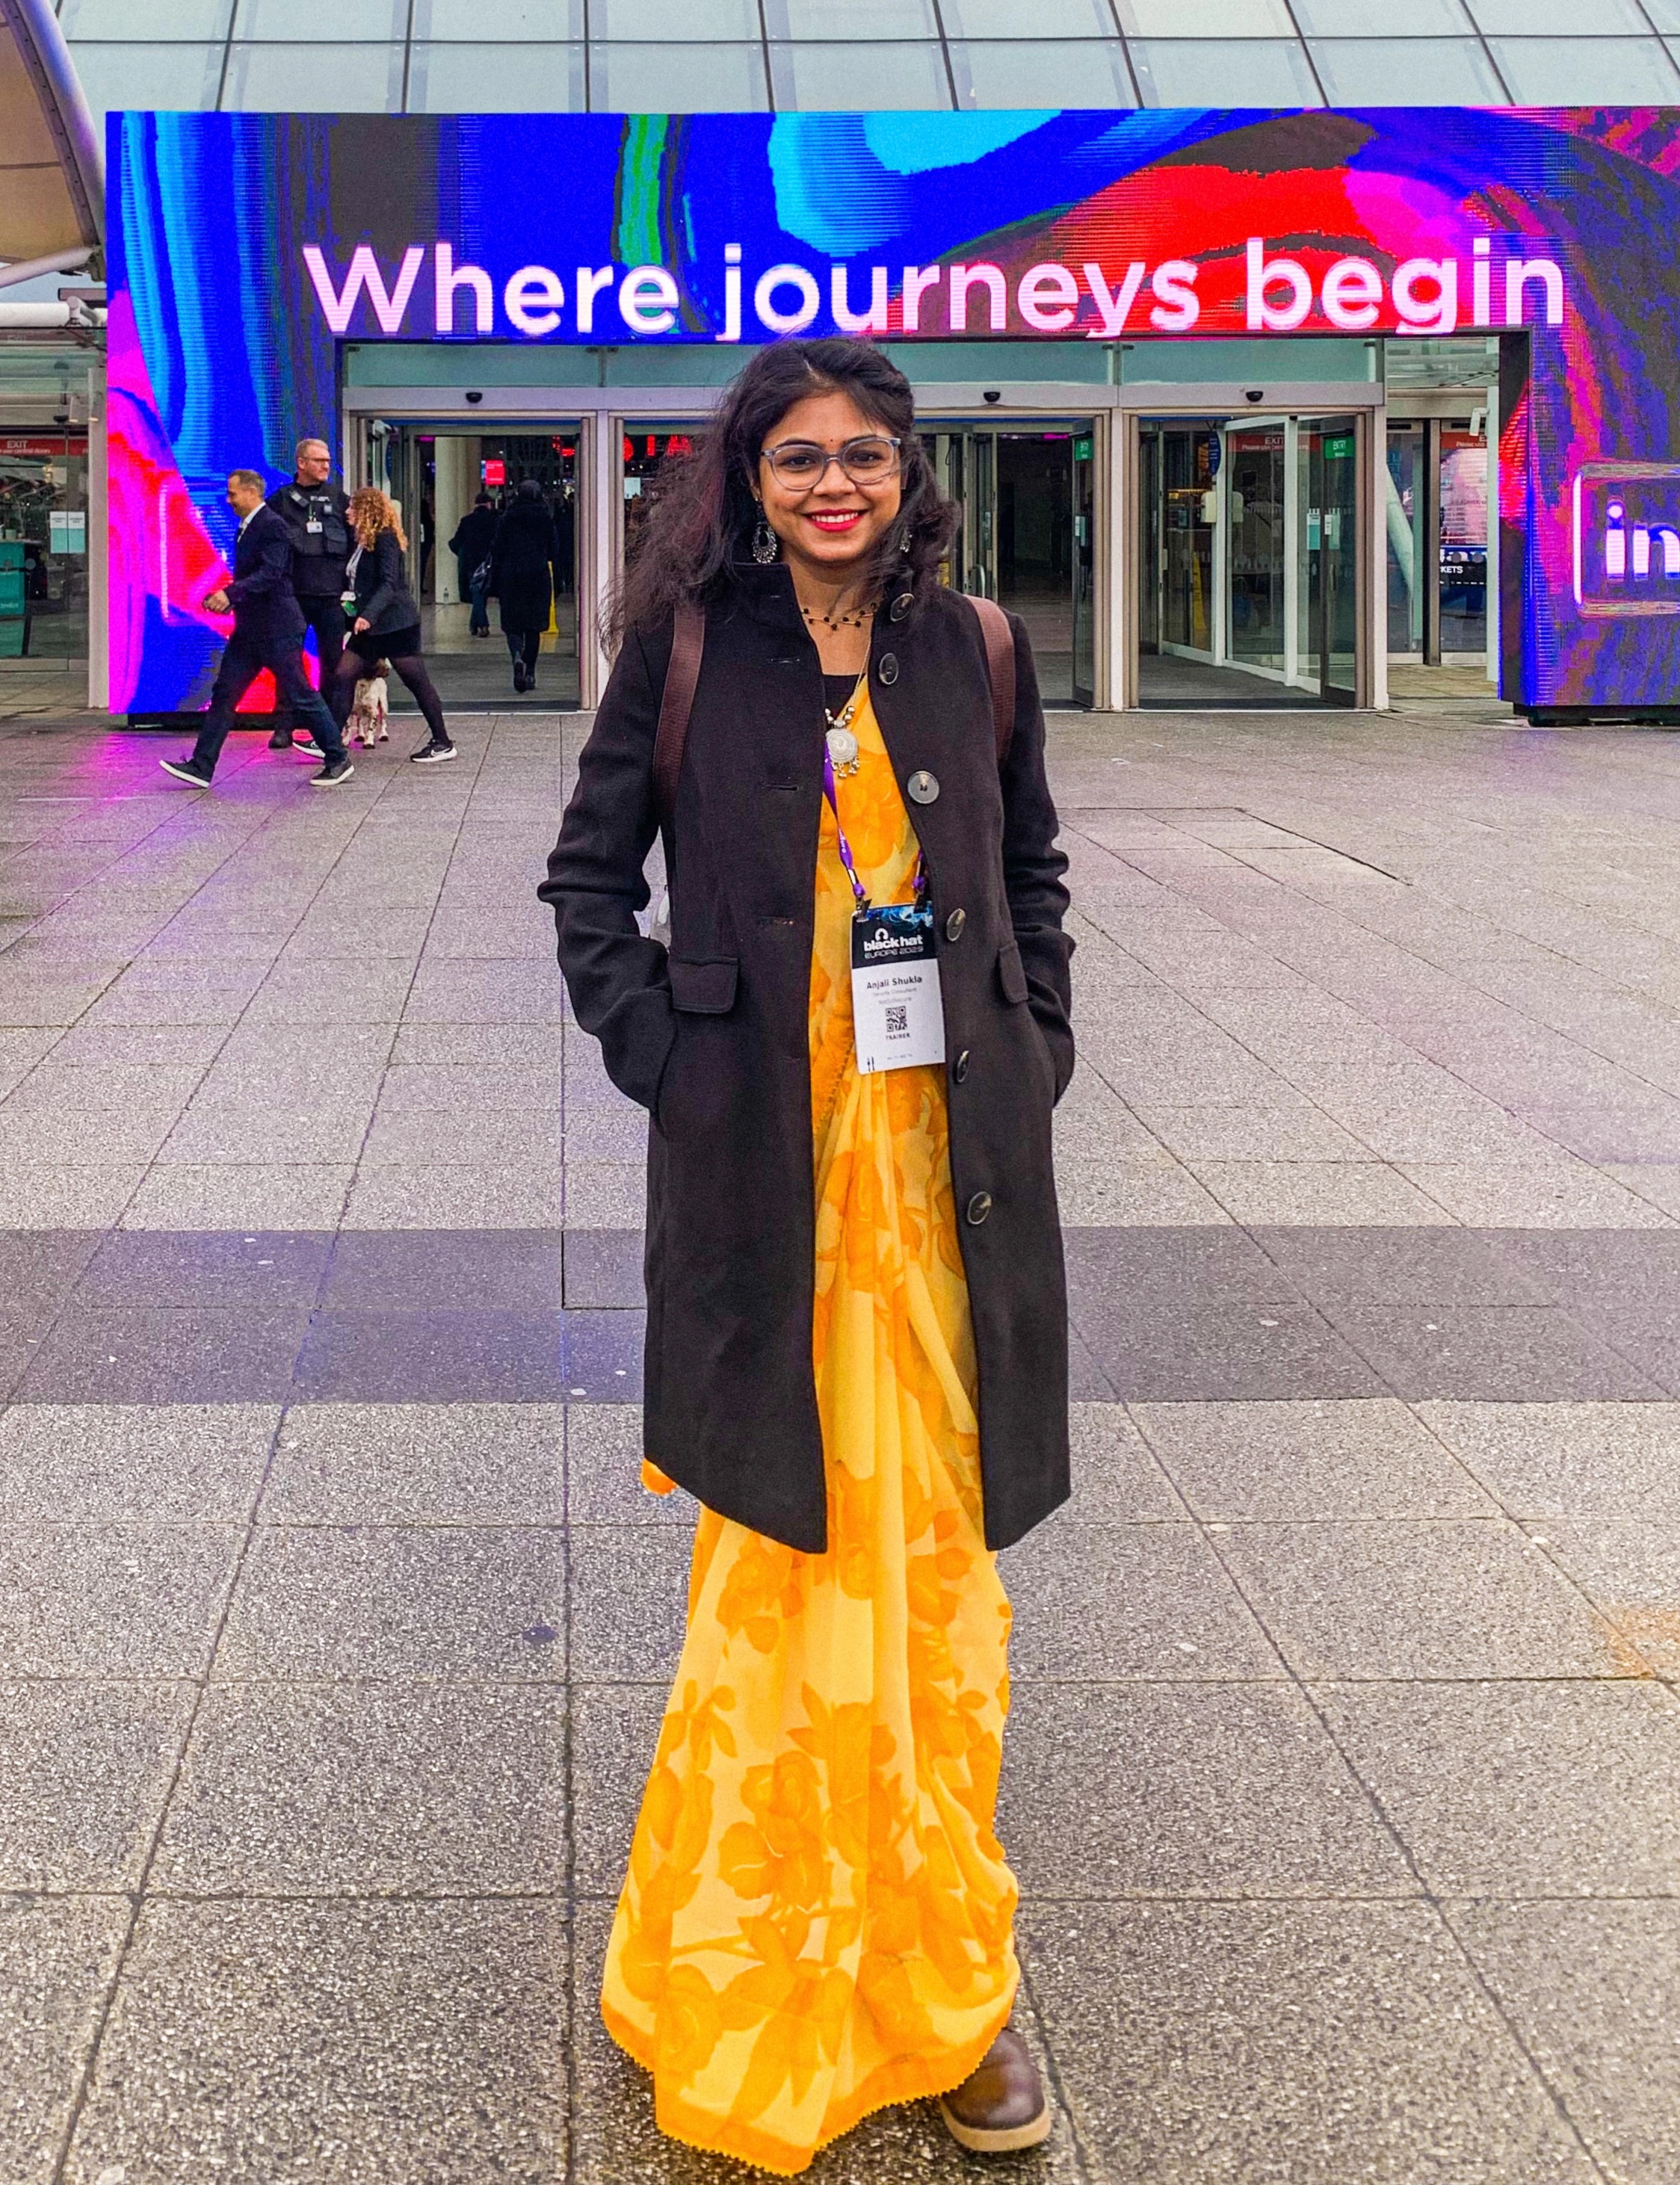
Anjali Shukla
Senior Security Engineer · Black Hat and Nullcon trainer
Founder, Container Security Village. OWASP EKS Goat lead. AWS Community Builder. Women Influencer in Cloud Security, CSA Bangalore 2023. Leads the W3-CS Bengaluru chapter.
Questions
Do I need my own AWS account?
No. The AWS labs run in environments we provide, and the rest runs in GitHub Codespaces. You need a GitHub account and a browser.
Is it beginner-friendly?
Yes, if you are comfortable on the command line and can follow step-by-step instructions. You do not need prior security experience - each section starts from the fundamentals before the labs get adversarial.
What if I miss a day?
We will move you into a future batch or another course instead. Fees are non-refundable.
How long do I keep the book?
The mdbook is yours to keep, for good.
Can I get a refund?
Fees are non-refundable. If you cannot attend for documented medical reasons you can request to transfer your seat to another person, chargeable at 10% of the fee and subject to written approval. Full terms are on the refund and cancellation policy page.
Will the batch definitely run?
The batch runs with a minimum of 2 participants and is capped at 35. If it cannot run we contact you before the date.
Fees, transfers and cancellations in full on the refund and cancellation policy page.