Hands-On AI, LLM & MCP Red Teaming
Red team the AI surface: prompt injection, RAG poisoning, and the tool-use and MCP paths that turn a model into a foothold. Then put the guardrails back: least-privilege tool scoping, input and output filtering, and monitoring built for LLM applications.
- Format
- Online, live
- Labs
- Browser-based
- Next batch
- Not scheduled
We will write once, when a date is set.
About this training
LLM-backed applications ship with a new attack surface: the prompt, the retrieved context, the tools a model can call, and the MCP servers it talks to. This training walks that surface end to end, attacking it first and then closing it.
Day one is offence: prompt injection, RAG and context poisoning, tool-use and agent abuse, and MCP exploitation. Day two is defence: guardrails and filtering, least-privilege tool and agent design, monitoring for LLM apps, and hardening an MCP deployment.
Key aspects of the workshop include:
- Run direct and indirect prompt injection against a live agent
- Poison a RAG pipeline and exfiltrate data through retrieved context
- Abuse function-calling and tool permissions to escalate an agent's reach
- Exploit a vulnerable MCP server's tools and resources
- Build and test input and output guardrails that hold up under attack
- Scope tools and agents to least privilege, with a human in the loop where it matters
- Instrument an LLM application for monitoring and anomaly detection
- Harden an MCP deployment and leave with a red-team playbook to reuse
What you’ll do
19 labs and 6 theory sessions across 10 sections. Theory appears where it is needed for the next lab, not as a lecture block.
01Setup and Fundamentals
- theoryLLM application architecture and where the attack surface actually is
- labEnvironment setup: sandbox model access and tooling
02Prompt Injection Attacks
- labDirect prompt injection against a live agent
- labIndirect prompt injection via a poisoned document
- theoryWhy instruction and data stay mixed in a single context window
03RAG and Context Poisoning
- labPoison a RAG pipeline's source documents
- labExfiltrate data through retrieved context
- labCross-session context leakage
04Tool Use and Agent Abuse
- labEscalate an agent's reach through over-scoped function calls
- labChain tool calls into an unintended action
- theoryWhy an agent's tools need the same review as an API
05MCP Exploitation
- labEnumerate a Model Context Protocol server's tools and resources
- labExploit a vulnerable MCP tool
- labAbuse an over-permissioned MCP resource
06Guardrails and Filtering
- labBuild input and output guardrails
- labTest guardrails against the day one attacks
- theoryWhere filtering helps, and where it cannot
07Secure Agent and Tool Design
- labScope tools and agents to least privilege
- labAdd a human-in-the-loop checkpoint to a sensitive action
08Monitoring and Detection
- labInstrument an LLM application for logging and tracing
- labBuild a simple anomaly detection rule for prompt injection attempts
09Secure MCP Deployment
- labHarden an MCP server's tool and resource permissions
- labCleanup
10Red Team Wrap-up
- theoryBuilding an internal AI red-team playbook
- theoryWhere this fits alongside existing AppSec and pentest practice
Read the prerequisites before you book.
Some trainings require you to bring your own cloud account (AWS, GCP, or both) with billing enabled and admin privileges. Labs will not run without it, so confirm you meet every prerequisite below before the session.
Hard requirement for corporate laptops: admin permission to install tools, endpoint security and antivirus disabled, and the required lab domains not blocked on your network. Confirm this with your IT team before you register - troubleshooting a locked-down laptop mid-session is not possible.
How our trainings run
- Live and instructor-led, with the trainers in the room rather than a recording.
- Labs run in the browser. Nothing to install, and no fight with a corporate laptop.
- Attack first, then fix. Every exploited flaw is followed by the control that stops it.
- You keep the material and a certificate of completion.
Who runs it
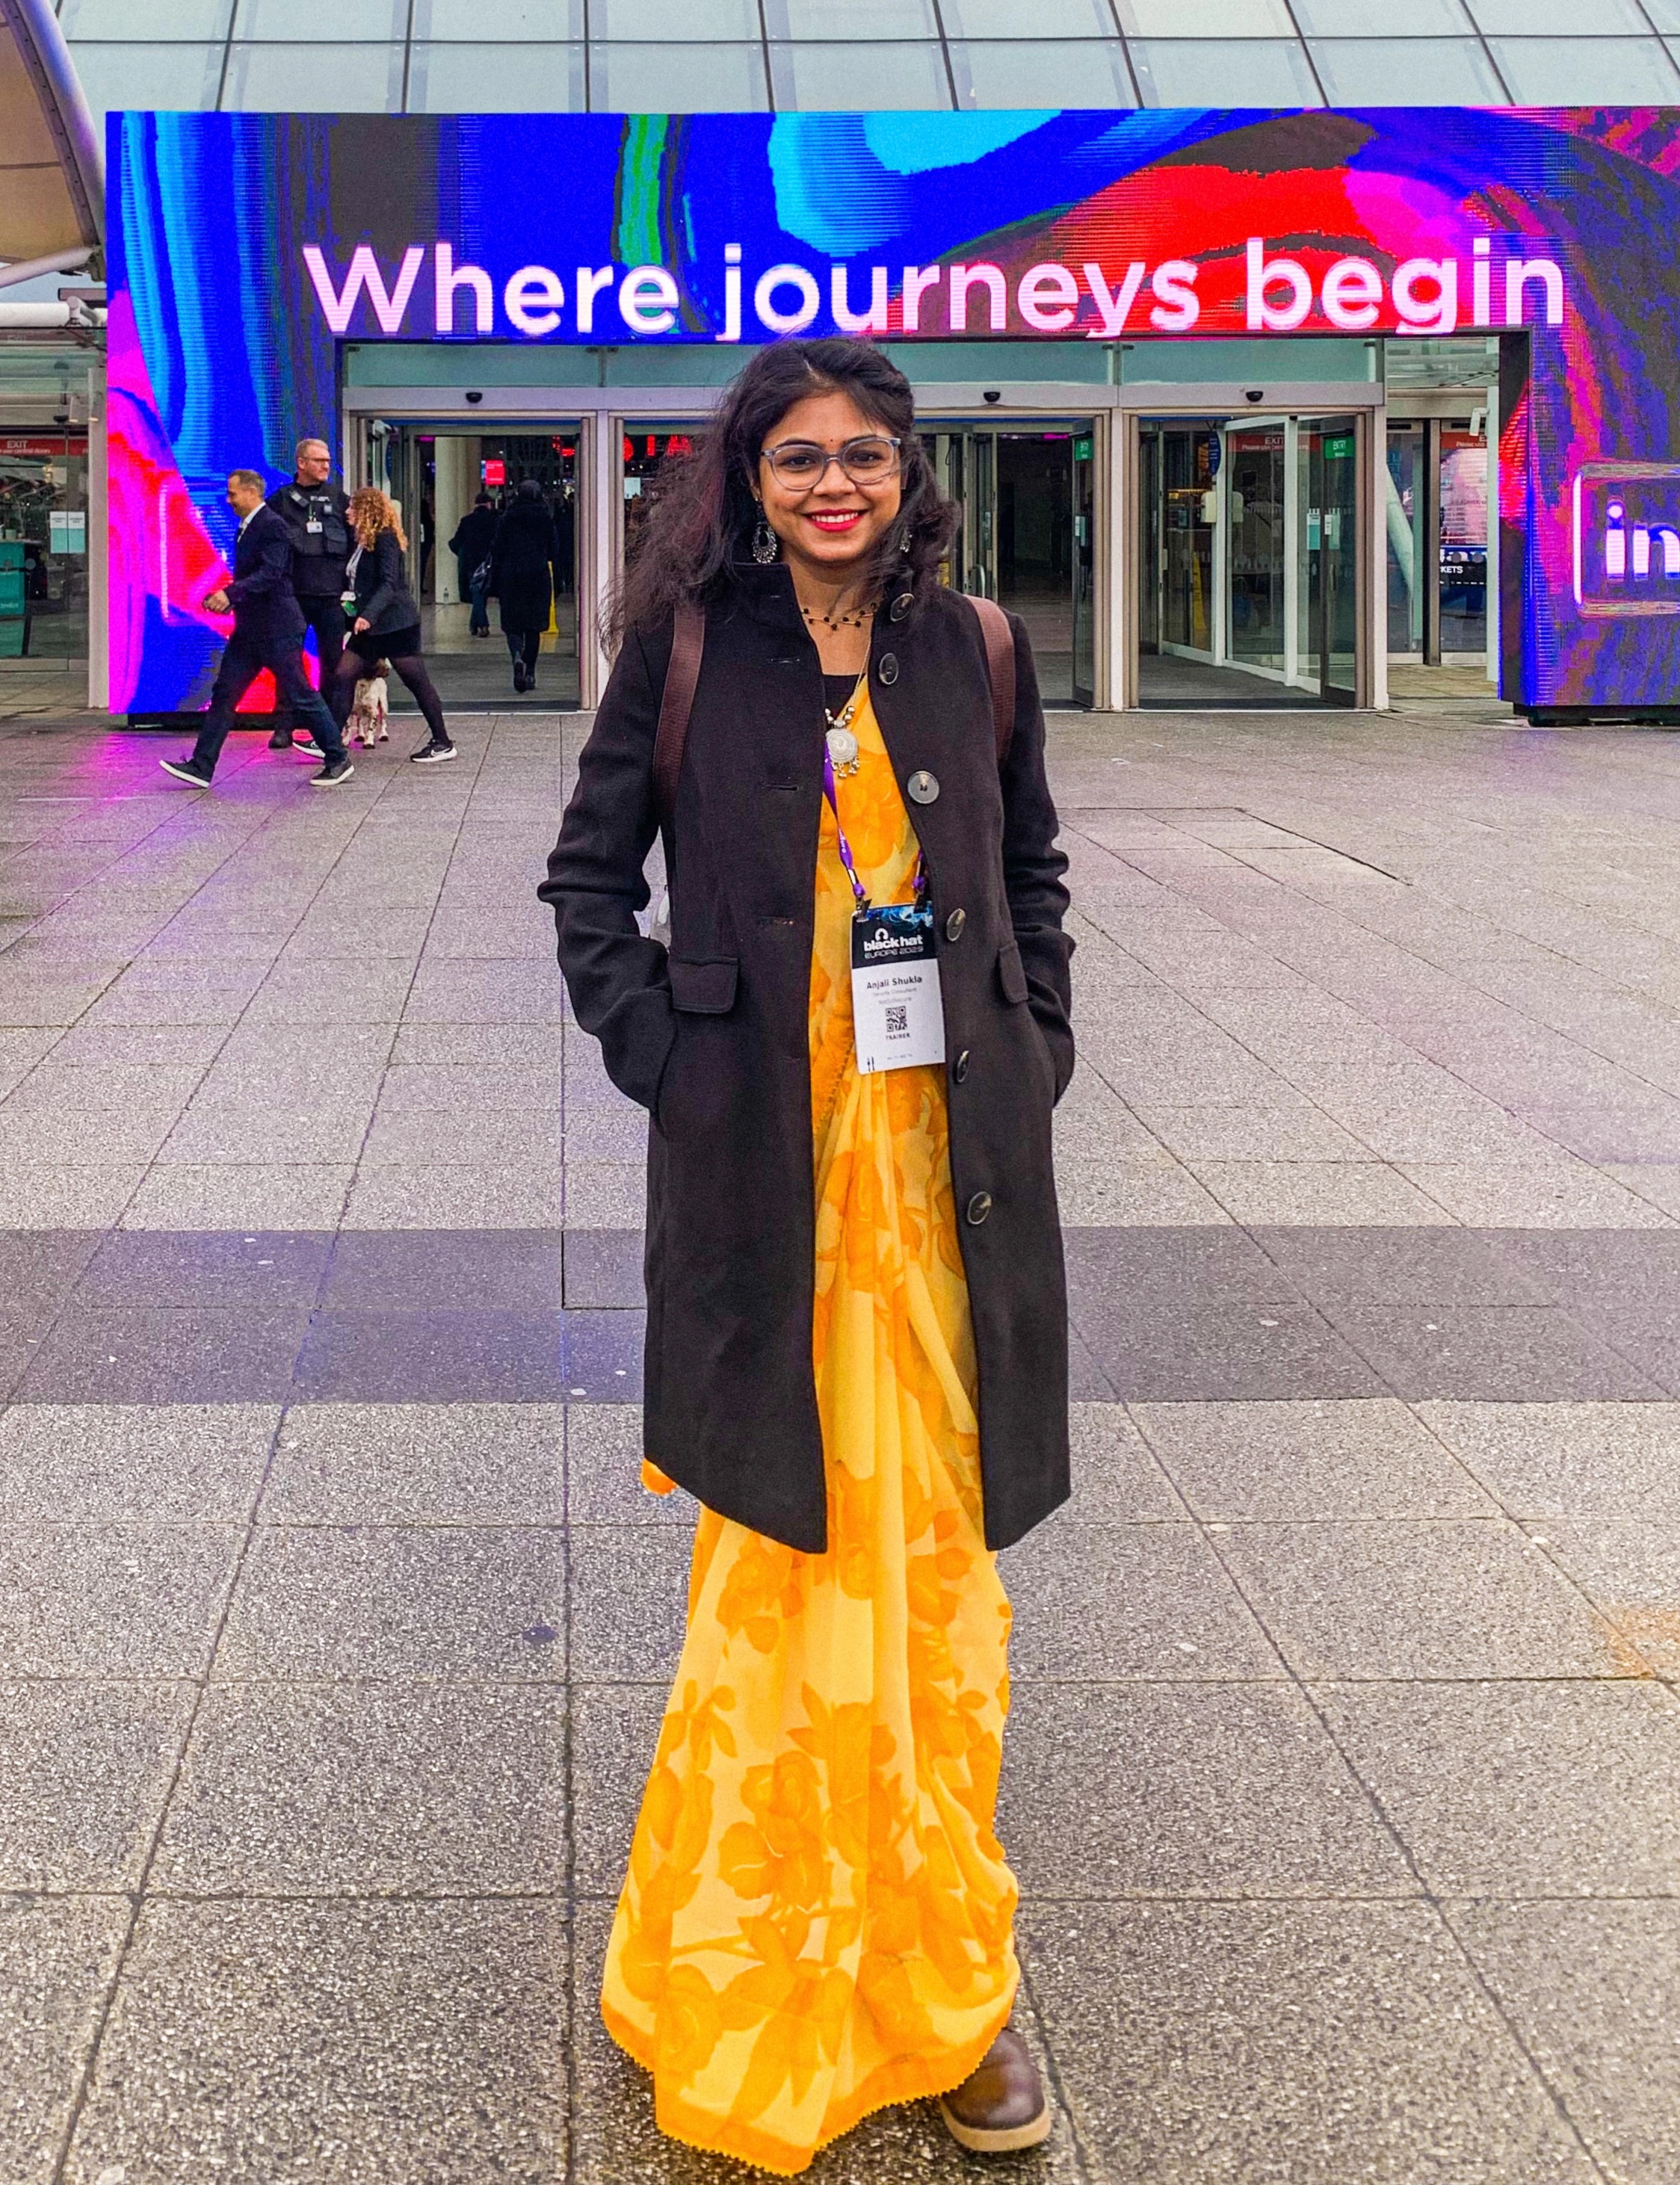
Anjali Shukla
Senior Security Engineer · Black Hat and Nullcon trainer
Founder, Container Security Village. OWASP EKS Goat lead. AWS Community Builder. Women Influencer in Cloud Security, CSA Bangalore 2023. Leads the W3-CS Bengaluru chapter.
Want a seat when it runs?
This batch is not scheduled yet. Join the waitlist and we will write the moment a date is set.
Support Our Work
Subscribe, like, and share our videos.
No Spam. Only updates.