Offensive Container Security
Break out of a container, then close every door you just walked through: namespaces, capabilities, and the image layers attackers dig through. Lock it down again with SBOM generation, image CVE scanning with Trivy, and secure Dockerfile defaults you can take back to your own pipeline.
Delivered as a workshop at:
- Format
- Online, live
- Labs
- Browser-based
- Next batch
- Not scheduled
We will write once, when a date is set.
About this training
Containers are the unit almost everything ships in now, and most of their security lives in defaults nobody set on purpose. This workshop works through those defaults from both sides.
You start with what a container actually is against a virtual machine, how an image is built and delivered, and what the host boundary really guarantees. Then you cross it: host mounts, privileged containers and Linux capabilities. The rest is closing what you opened, with static analysis, CVE scanning, an SBOM, and a set of secure defaults you can take back.
What you’ll do
9 labs and 7 theory sessions across 7 sections. Theory appears where it is needed for the next lab, not as a lecture block.
01Setup
- labSet up a GitHub Codespace
02Foundations
- theoryContainers and virtual machines
- theoryImages and running containers
- theoryDockerfile
- theoryDocker architecture
- labDockerfile static analysis
- labDocker Compose basics
03Image build and delivery
- theoryRegistry and image lifecycle
- labSlim Python images
04Runtime risk
- theoryThe host boundary
- labAttacking host mounts and privileged containers
- labAttacking Linux capabilities
05Image audit
- theoryImage CVE scanners
- labTrivy image scan
06Supply chain
- labSBOM with Syft and Grype
07Hardening
- labSecure container defaults
Work through it yourself
The full workshop material is public. Work through it at your own pace, or use it to revisit the labs after a session.
containersecurity.peachycloudsecurity.com →Read the prerequisites before you book.
Some trainings require you to bring your own cloud account (AWS, GCP, or both) with billing enabled and admin privileges. Labs will not run without it, so confirm you meet every prerequisite below before the session.
Hard requirement for corporate laptops: admin permission to install tools, endpoint security and antivirus disabled, and the required lab domains not blocked on your network. Confirm this with your IT team before you register - troubleshooting a locked-down laptop mid-session is not possible.
How our trainings run
- Live and instructor-led, with the trainers in the room rather than a recording.
- Labs run in the browser. Nothing to install, and no fight with a corporate laptop.
- Attack first, then fix. Every exploited flaw is followed by the control that stops it.
- You keep the material and a certificate of completion.
Who runs it
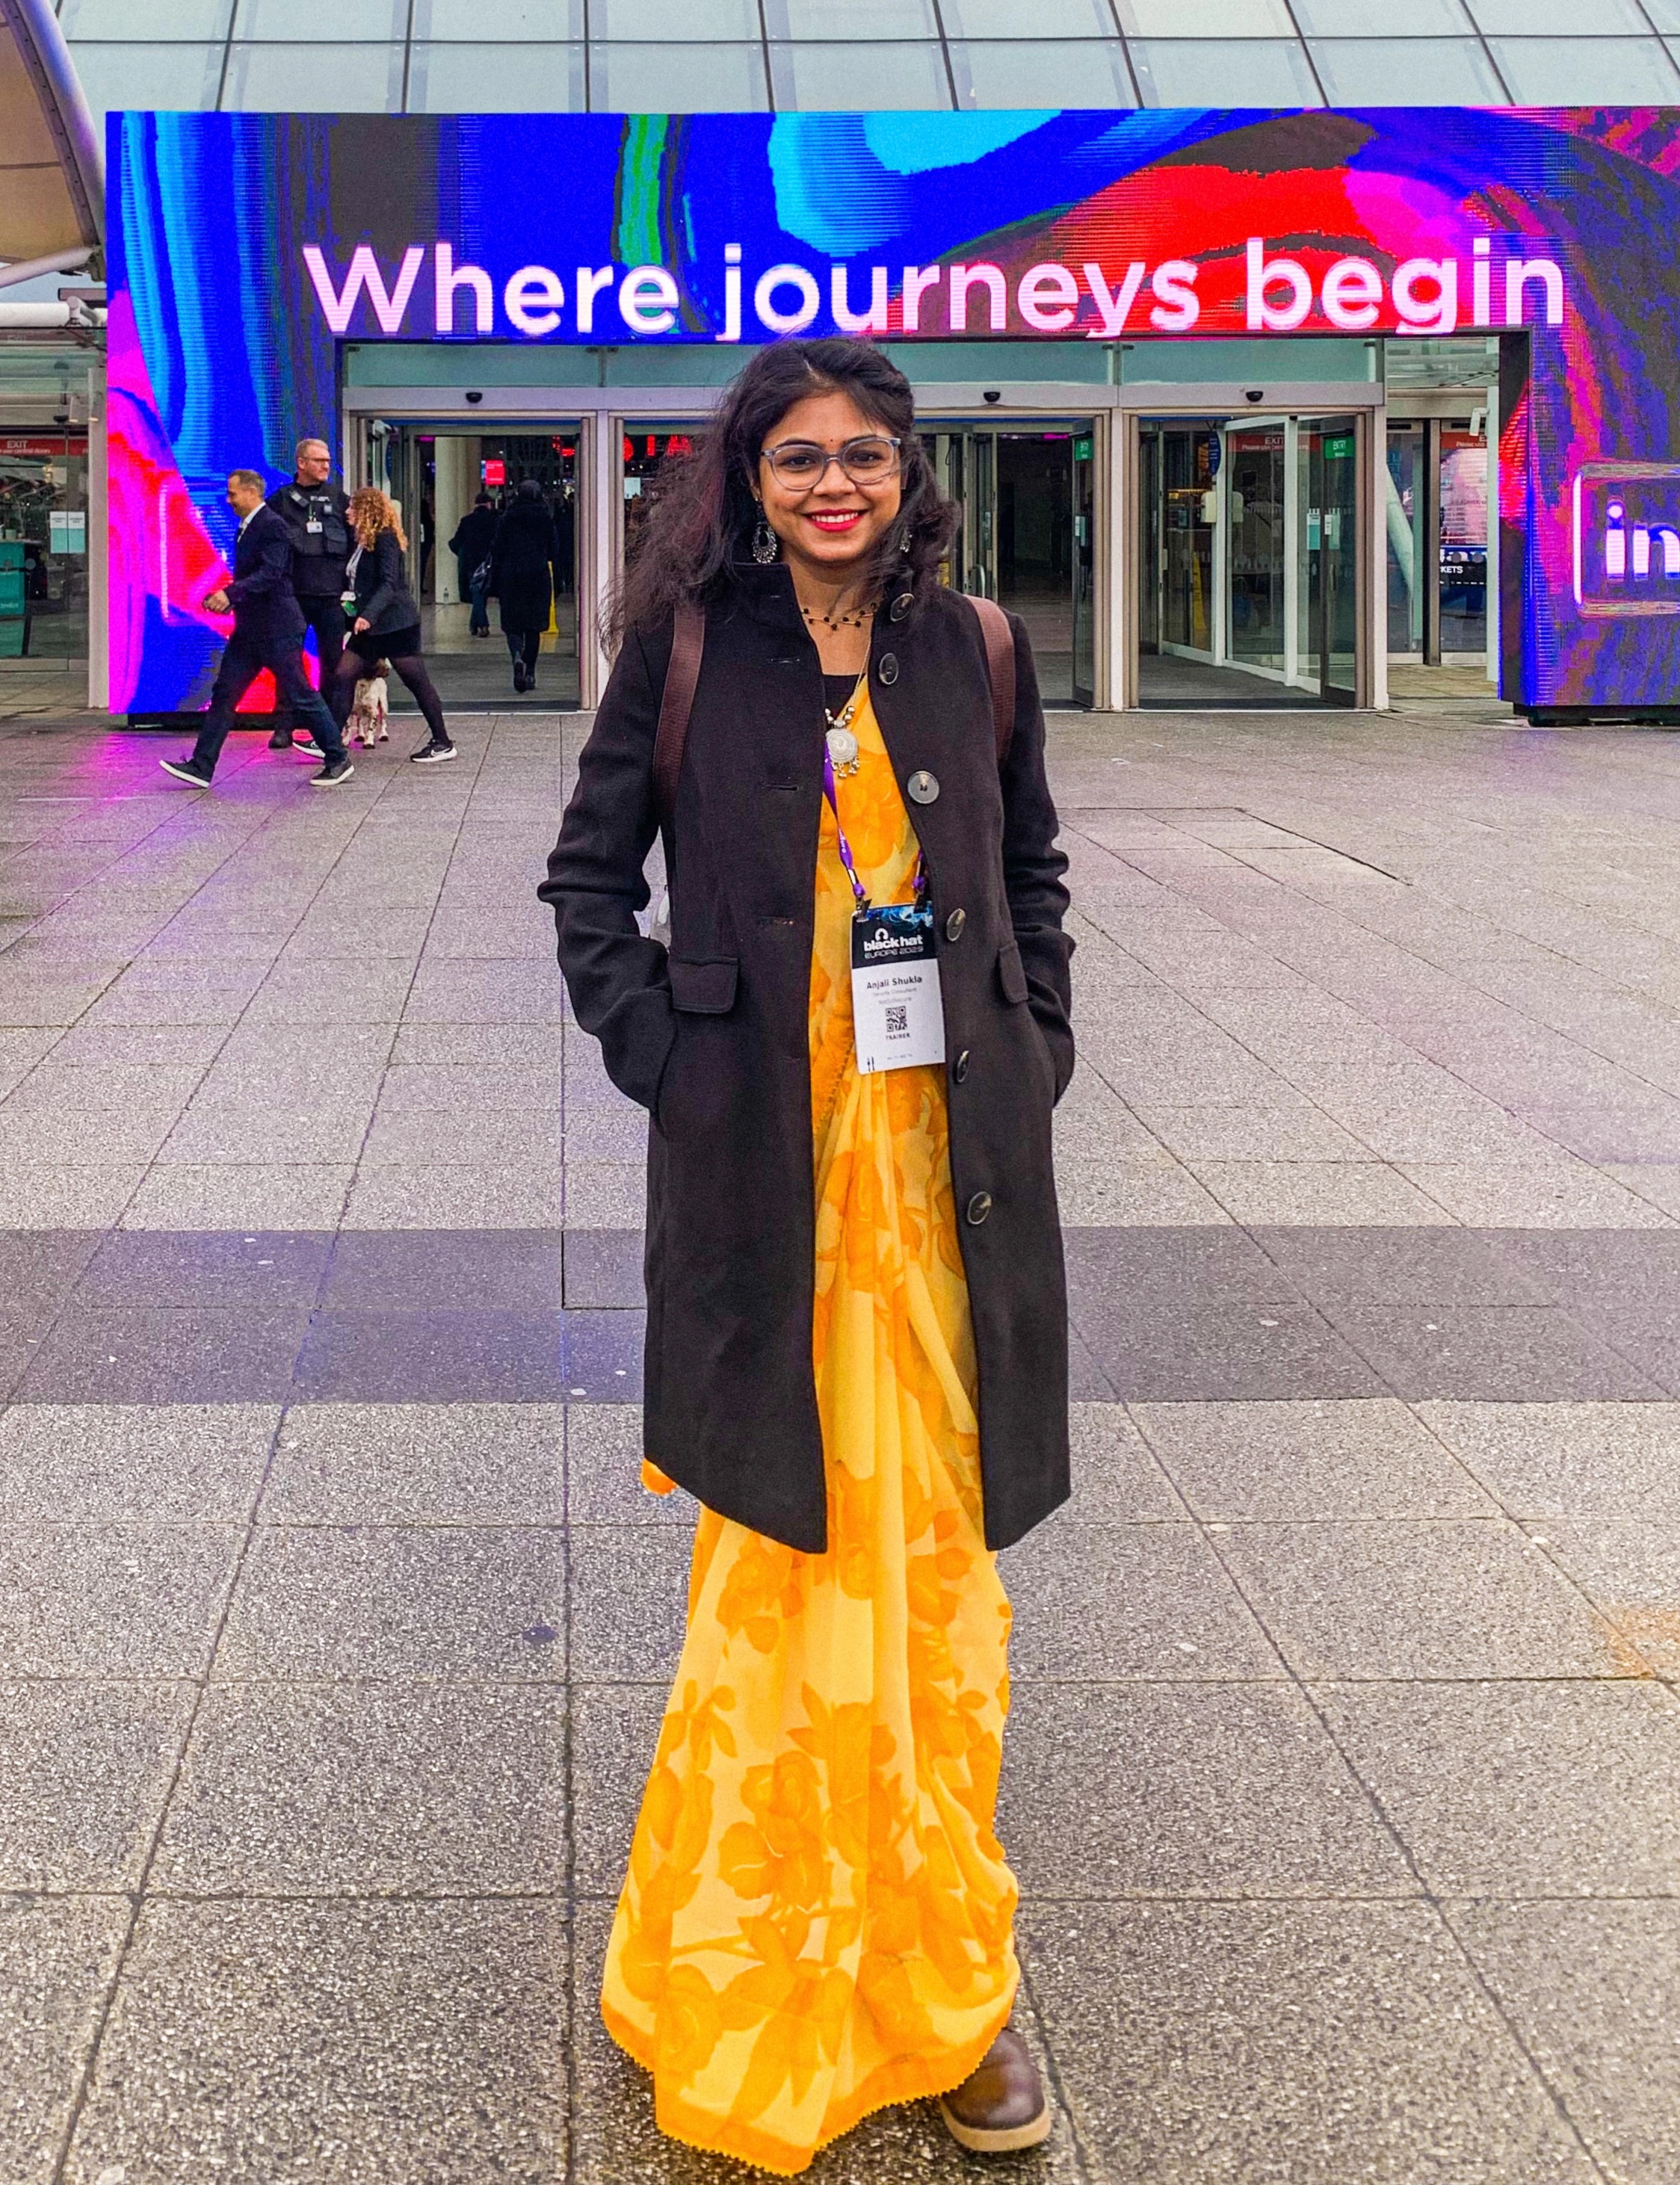
Anjali Shukla
Senior Security Engineer · Black Hat and Nullcon trainer
Founder, Container Security Village. OWASP EKS Goat lead. AWS Community Builder. Women Influencer in Cloud Security, CSA Bangalore 2023. Leads the W3-CS Bengaluru chapter.
Want a seat when it runs?
This batch is not scheduled yet. Join the waitlist and we will write the moment a date is set.
Support Our Work
Subscribe, like, and share our videos.
No Spam. Only updates.