Ace Your Cloud Security Interview with Hands-on Assignment
In this hands-on workshop, you'll tackle real-world AppSec scenarios through interactive mock interviews. Practice explaining OWASP Top 10 findings, cloud misconfigurations and secure code review out loud, and get direct feedback on how you would perform in a live technical round.
- Format
- Online, live
- Labs
- Browser-based
- Next batch
- Not scheduled
We will write once, when a date is set.
Outline coming soon
We are writing the lab-by-lab outline for this one. Join the waitlist and you get it as soon as it is published, along with the dates.
Read the prerequisites before you book.
Some trainings require you to bring your own cloud account (AWS, GCP, or both) with billing enabled and admin privileges. Labs will not run without it, so confirm you meet every prerequisite below before the session.
Hard requirement for corporate laptops: admin permission to install tools, endpoint security and antivirus disabled, and the required lab domains not blocked on your network. Confirm this with your IT team before you register - troubleshooting a locked-down laptop mid-session is not possible.
How our trainings run
- Live and instructor-led, with the trainers in the room rather than a recording.
- Labs run in the browser. Nothing to install, and no fight with a corporate laptop.
- Attack first, then fix. Every exploited flaw is followed by the control that stops it.
- You keep the material and a certificate of completion.
Who runs it
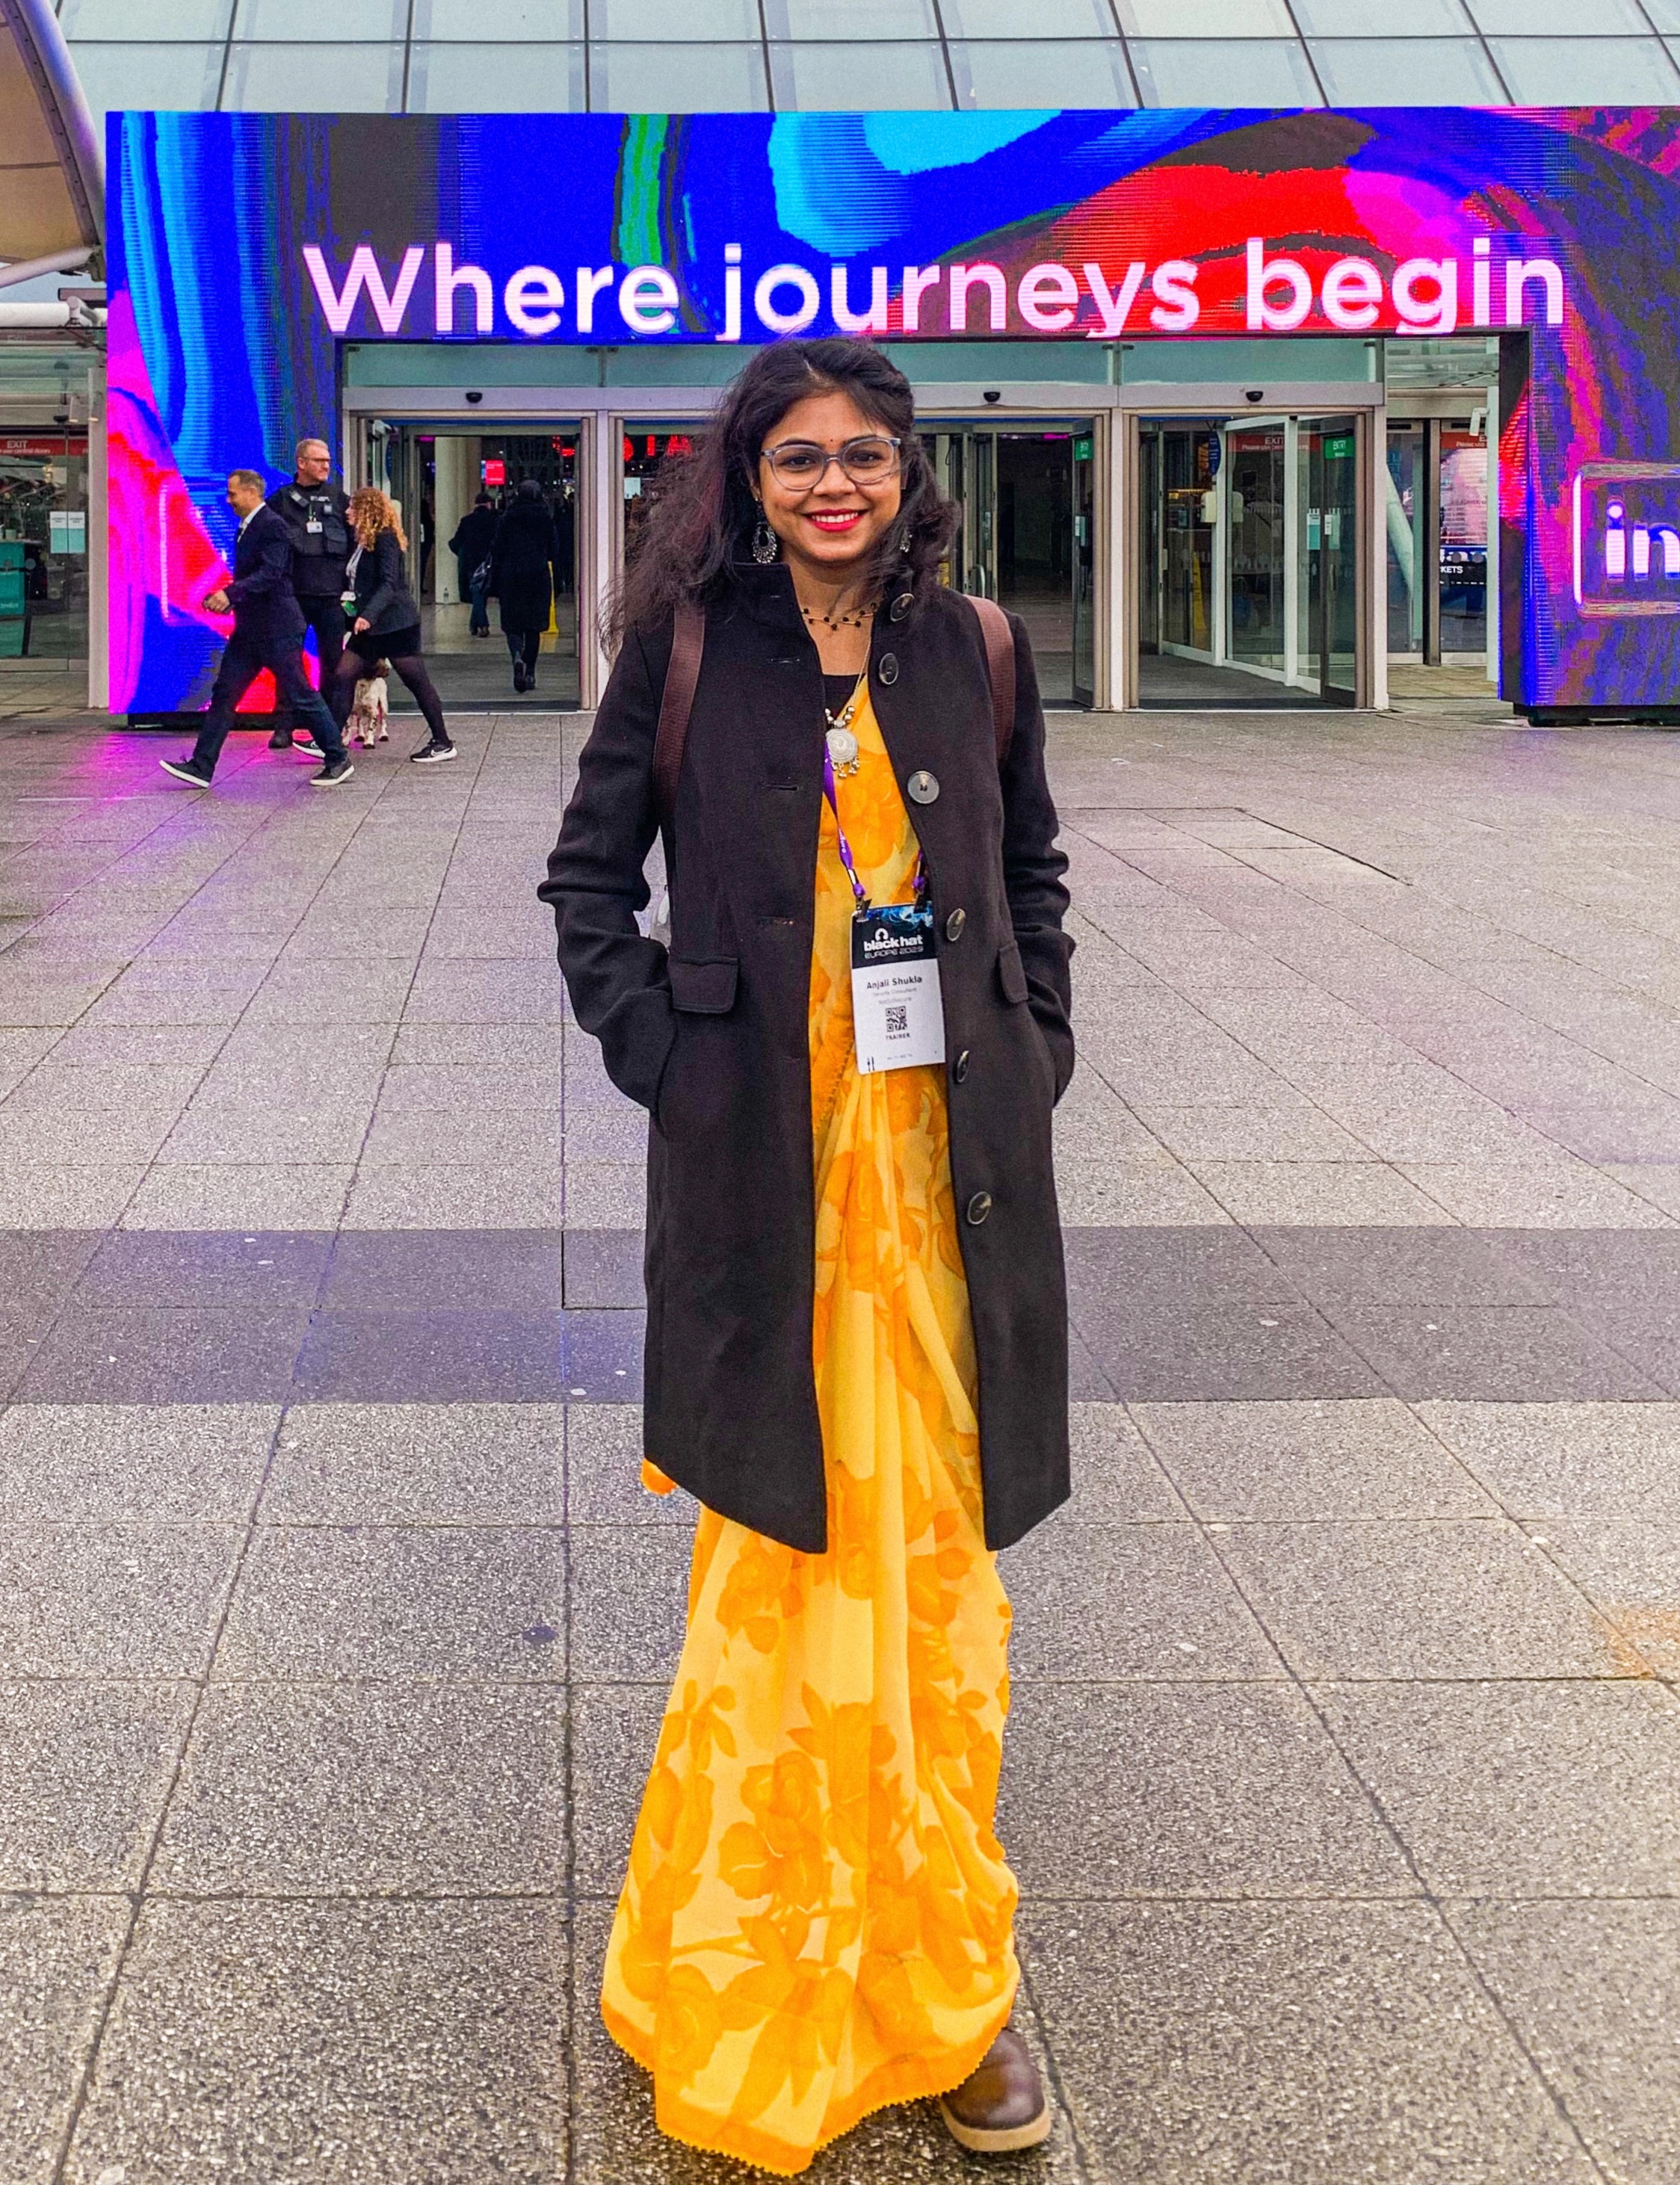
Anjali Shukla
Senior Security Engineer · Black Hat and Nullcon trainer
Founder, Container Security Village. OWASP EKS Goat lead. AWS Community Builder. Women Influencer in Cloud Security, CSA Bangalore 2023. Leads the W3-CS Bengaluru chapter.
Want a seat when it runs?
This batch is not scheduled yet. Join the waitlist and we will write the moment a date is set.
Support Our Work
Subscribe, like, and share our videos.
No Spam. Only updates.